Sandboxing Untrusted Code Execution in Agent Pipelines
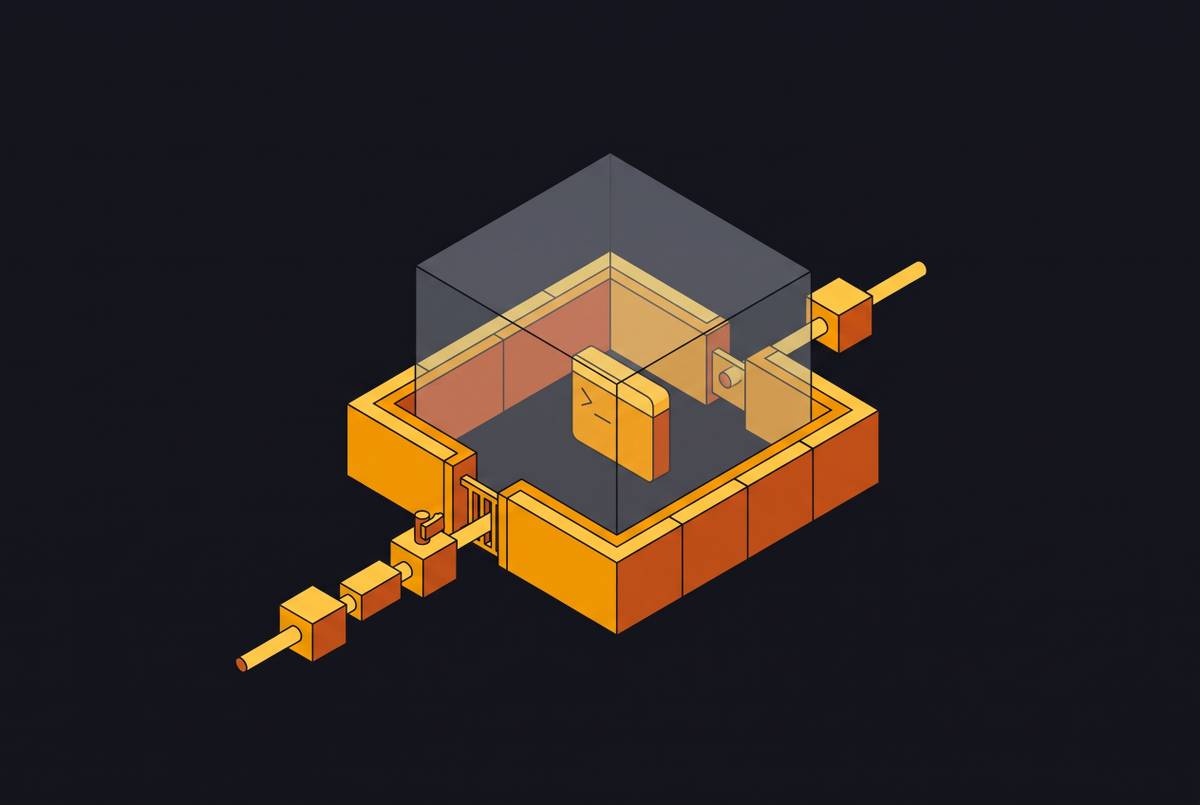
Runtime isolation for AI-generated code requires VM boundaries plus controls above the sandbox.
Yuki Tanaka-Osei
Attackers exploit every stage of retrieval pipelines to steal sensitive data.
Runtime isolation for AI-generated code requires VM boundaries plus controls above the sandbox.
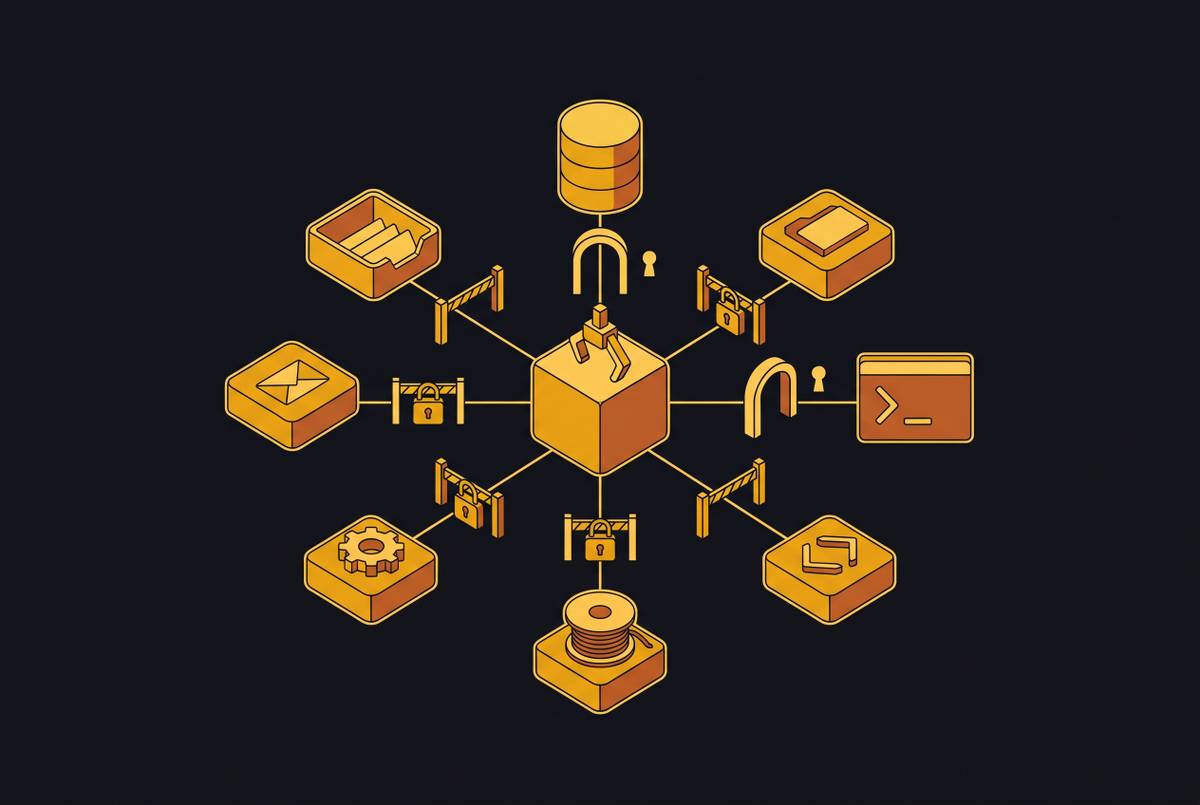
AI agents need permission controls designed for their speed and scope, not human role models.
How to build logging that captures what agents do and why it matters.
Detect, contain, and roll back all four artifact layers together.