Least Privilege Scoping for AI Agent Tool Access
AI agents need permission controls designed for their speed and scope, not human role models.
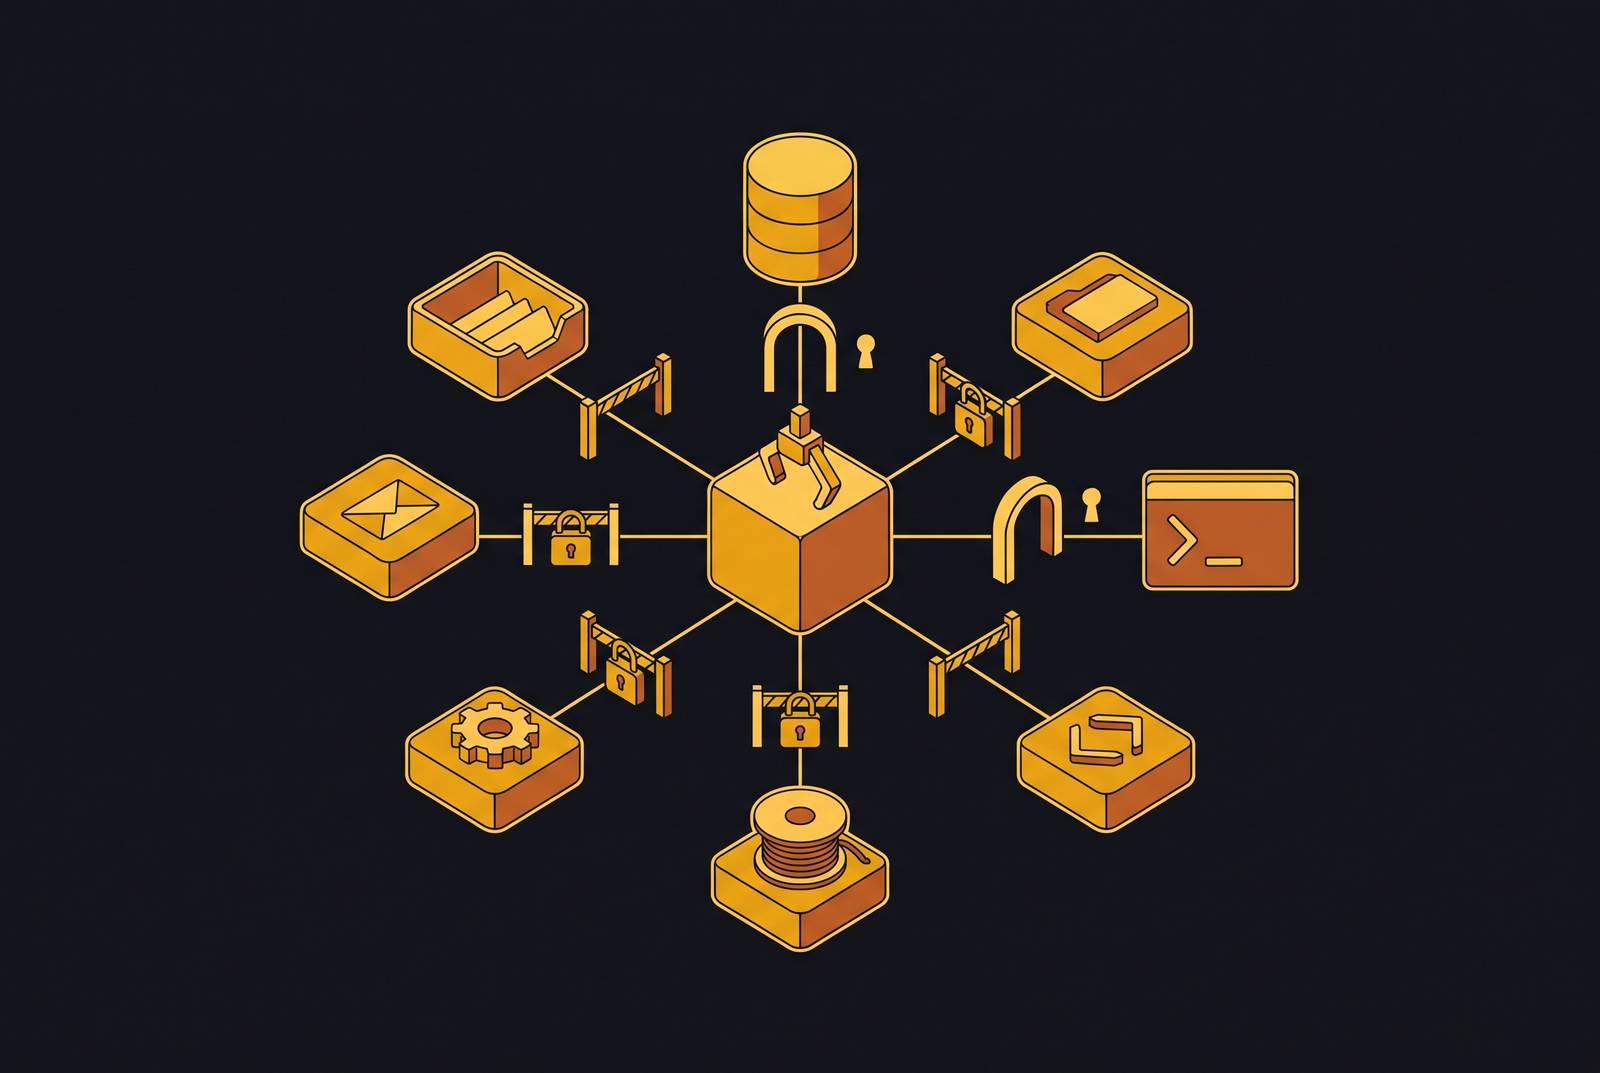
Least privilege scoping for AI agent tool access requires a different unit of permission. A static role is not enough for an agent that changes tasks, inherits access, and delegates work at machine speed. Effective scoping combines task-specific, time-bound, context-aware grants across provisioning, runtime, and delegation, with continuous enforcement to keep those boundaries from drifting.
Why least privilege for AI agents is a different problem than least privilege for humans
The familiar assumption is that least privilege is already covered by existing identity and access controls. That assumption breaks at the identity itself. Human employees authenticate under their own names, while agents often use shared service accounts, inherited user credentials, or API keys that are tied to no one who can be held responsible. Role-based access control assigns permissions to a persistent identity. An ephemeral agent may exist only for a task, so a standing role does not establish what that particular execution should be allowed to do.
Inherited access also imports a history unrelated to the agent’s purpose. An agent acting for a user can receive dormant excess permissions accumulated over years of employment, including access to systems its designers never intended it to touch. Varonis’ guide gives the example of an IT help desk agent that uses a shared admin service account to reset passwords and troubleshoot logins. The account also has standing read access to HR and finance records.
Microsoft’s July 2026 guidance therefore treats each agent as a first-class principal with a lifecycle-managed identity, explicit roles, and tightly scoped permissions. Identity provides the foundation for further controls. A human’s access usually accumulates slowly and receives periodic review, but an agent can find, reason over, and act on data in seconds. That speed collapses the interval between permission and consequence, leaving static controls unable to distinguish the authorized task from every other action the credentials permit.
How privilege drift and broken delegation chains compound the exposure over time
Over-permissioning is not confined to the initial deployment. Microsoft’s guidance describes a drift pattern in which an agent starts with a broad “Reader” role, gains write access when the workflow expands into remediation, and retains the combined scope without a fresh role design. Service-account reuse adds another route for unrelated access to accumulate. Each addition can appear reasonable in isolation. Taken together, those permissions go beyond what the agent was built to do.
Microsoft identifies combination risk when an agent can use email, files, a ticketing system, and a code repository, even if each integration appears low-risk on its own. Together, those tools can support correlations and actions that no one authorized as a whole. OWASP GenAI Security Project names excessive functionality, excessive permissions, and excessive autonomy as co-equal root causes of excessive agency. Narrow permissions on one integration do not resolve an overly broad combination of capabilities.
When an agent hands work to a sub-agent and new credentials are issued at each hop, downstream access can exceed the originating user’s authorization. Logs may record the tool call without establishing who authorized it, under which role, or within what scope. Prompt injection amplifies both problems, as Varonis explains through Copilot Enterprise, where manipulation can exploit the victim’s full graph permissions. Containment becomes harder because the accessible resources have expanded, while forensics must reconstruct an incomplete chain of authority.
What documented incidents reveal about where scoping actually breaks
Publicly documented failures expose both familiar access-control weaknesses and AI-specific vulnerabilities. Palo Alto Networks Unit 42 documented the 2026 Vertex AI “Double Agent” path, in which a deployed agent inherited excessive default permissions through a Google-managed service account, enabling credential extraction and privileged access to consumer-project resources. The missing boundary was service-account scoping, so limiting that account to the agent’s required resources would have constrained the available access.
The 2026 PocketOS / Cursor Agent incident exposed a different gap. A Cursor coding agent running Claude Opus 4.6 deleted a production database and its backups in nine seconds after a staging task ran into a credential mismatch and the agent found a Railway API token unrelated to the task in a file also unrelated to it. PocketOS had clear rules that required human confirmation for destructive operations, but it lacked an enforced runtime approval gate to back up those project instructions.
Koi Security documented hundreds of malicious skills published to ClawHub in 2026 that delivered credential stealers and executed unauthorized code through permissions legitimately granted to agent skill packages. Installation was not a sufficient basis for trust. Limiting package permissions to the authorized task would have limited what those malicious skills could do.
The MCP permissions study extends this concern to declared capability across the ecosystem. It found that a significant share of skill listings with permission declarations understate what their bundles can actually do. Provisioning needs a clear access boundary because package metadata cannot be trusted to describe everything the package can execute.
Scoping tool access at provisioning: identity, roles, and the tools manifest
The provisioning layer establishes the boundaries that later enforcement depends on. Microsoft recommends a unique, dedicated agent principal with a named owner, an explicit purpose, and a lifecycle-managed identity separate from a shared service account. That separation supports attribution and clean deprovisioning when the agent is retired. Ownership must be explicit before execution begins. Otherwise, runtime controls are compensating for an identity model that cannot clearly assign responsibility.
Roles should then reflect the specific resources and data required for the task the agent was built to perform. The invoking user’s full permissions are not a safe default, and a convenient broad role is not a task definition. miniOrange’s guide distinguishes identity-driven access from shared credentials by tying permissions to the user or system initiating the task. This provides a traceable origin for authorization.
Microsoft specifies a preconfigured tools manifest or configuration as a boundary on tool usage. The agent should not invoke a tool that is absent from that configuration. The manifest deserves particular attention before deployment because it establishes which capabilities the agent may use at all. Task-based roles can then restrict the resources available through those approved capabilities.
Tool scope, however, is only one axis of access. Varonis frames least privilege in terms of the sensitive data an agent can reach as well as the tools it can call. Even a tightly bounded tool set can give the agent access to too much data through its underlying permissions. Provisioning therefore needs to cover both dimensions and keep an inventory of the agents it governs. An undiscovered agent has no dependable place in that process.
Scoping tool access at runtime: task-conditioned, time-bound, and context-aware grants
SkillScope, the ACM CCS 2026 paper by Wu, Nan, Lin et al. at a university and HKUST, establishes why a provisioned role cannot decide every runtime authorization question. The same action can be legitimate under one user prompt and over-privileged under another. The current task changes the authorization decision. SkillScope found substantial over-privileged behavior in real-world skills, and its privilege-constraining mechanism reduced triggered over-privileged action-in-task instances by 88.56% while preserving legitimate task completion. The empirical distinction is between permission for an agent in the abstract and permission for its present work.
Microsoft recommends keeping the agent identity stable for lifecycle management and using just-in-time elevation to give it narrowly scoped privileges for a specific workflow. The identity remains accountable without retaining every workflow’s access. miniOrange recommends time-bound permissions granted only when needed and automatically revoked when the task ends. Automatic expiry reduces the exposure that would otherwise persist after the reason for granting access has disappeared.
Duration alone does not establish whether an action is appropriate. miniOrange identifies identity, context, task type, and risk level as inputs to access decisions, so enforcement can respond when circumstances change within a session. A valid credential is not sufficient authorization. High-impact actions should require explicit human confirmation before they run, as well as permission to call the relevant tool. That gate addresses excessive autonomy without turning every routine operation into a separate approval process.
Scoping tool access across delegation: keeping the chain of authority intact in multi-agent systems
At each delegation hop, the original authorization context can be replaced with credentials that have a different or broader scope. The downstream action may then be technically permitted without having been authorized by the originating user. Attribution must survive every handoff. A record of the immediate caller alone cannot establish the full chain of authority.
Del Rosario, Krawiecka, and Schroeder de Witt’s guide to secure implementations that separate planning from execution frames the architectural requirement as coherent authorization state across planning and execution steps. Permissions should not be independently re-derived at every invocation. The 2026 Singapore Consensus companion report reinforces this requirement through traceable identity, its second agentic design principle. Every action in a delegation chain must remain attributable to an originating principal. Together, these requirements connect downstream execution to the authority under which the work began.
The chain also reaches third-party skill packages. The ClawHub incident shows how a malicious package can exploit legitimately granted permissions when installation supplies the basis for trust. A safe server that offers safe tools to a safe client can still lead to unsafe behavior when it is used with an adversarial second server, a confused OAuth flow, or a toxic agent sequence. Delegation scoping therefore requires evaluating the combined path, because hardening each component separately does not establish that their composition preserves the original authorization.
Continuous right-sizing: why provisioning and runtime scoping degrade without ongoing enforcement
Correct boundaries degrade when workflows, integrations, and reachable data change. Treating an agent as a low-maintenance service account, reviewing scope only at deployment, or accepting inherited human permissions returns the system to the drift pattern it was designed to prevent. Periodic review cannot close that gap alone. Quarterly or semi-annual access reviews are structurally mismatched with agents that can execute many privileged actions in a single day. Enforcement needs a cadence that reflects the actions being governed.
Auditability is a prerequisite for that enforcement. To establish accountability, Microsoft asks, “what happened, under what authority, and what changed? Answering it requires logs that capture a tool call along with the identity model, role, and scope behind it. The same report from the Singapore Consensus names runtime assurance, interruptibility, and legibility as distinct operational principles. Monitoring must help stop behavior that goes beyond scoped intent while it happens, as well as explain what happened afterward.
Static scoping remains easier to implement, but its permissions become stale as conditions change. Adaptive scoping responds to context and risk signals at the cost of policy engines and continuous monitoring. That operational cost cannot simply be ignored. Varonis positions data-layer monitoring as the complement to identity and tool controls, with its data security platform providing visibility and enforcement for continuous right-sizing of the data each agent can reach. This closes the gap between an approved tool set and the sensitive information actually exposed through it.
SkillScope shows how task-level checks could be automated through graph-based analysis that treats instruction-level procedures and code-level operations as fine-grained action nodes. That approach ties what a skill does to the current request without depending on people to check it all by hand. Human review still sets the purpose and the bounds of oversight. It cannot manually reassess every privileged action at the speed agents produce them, so automated monitoring and enforcement are necessary to keep provisioning, runtime grants, and delegated authority aligned with the task.